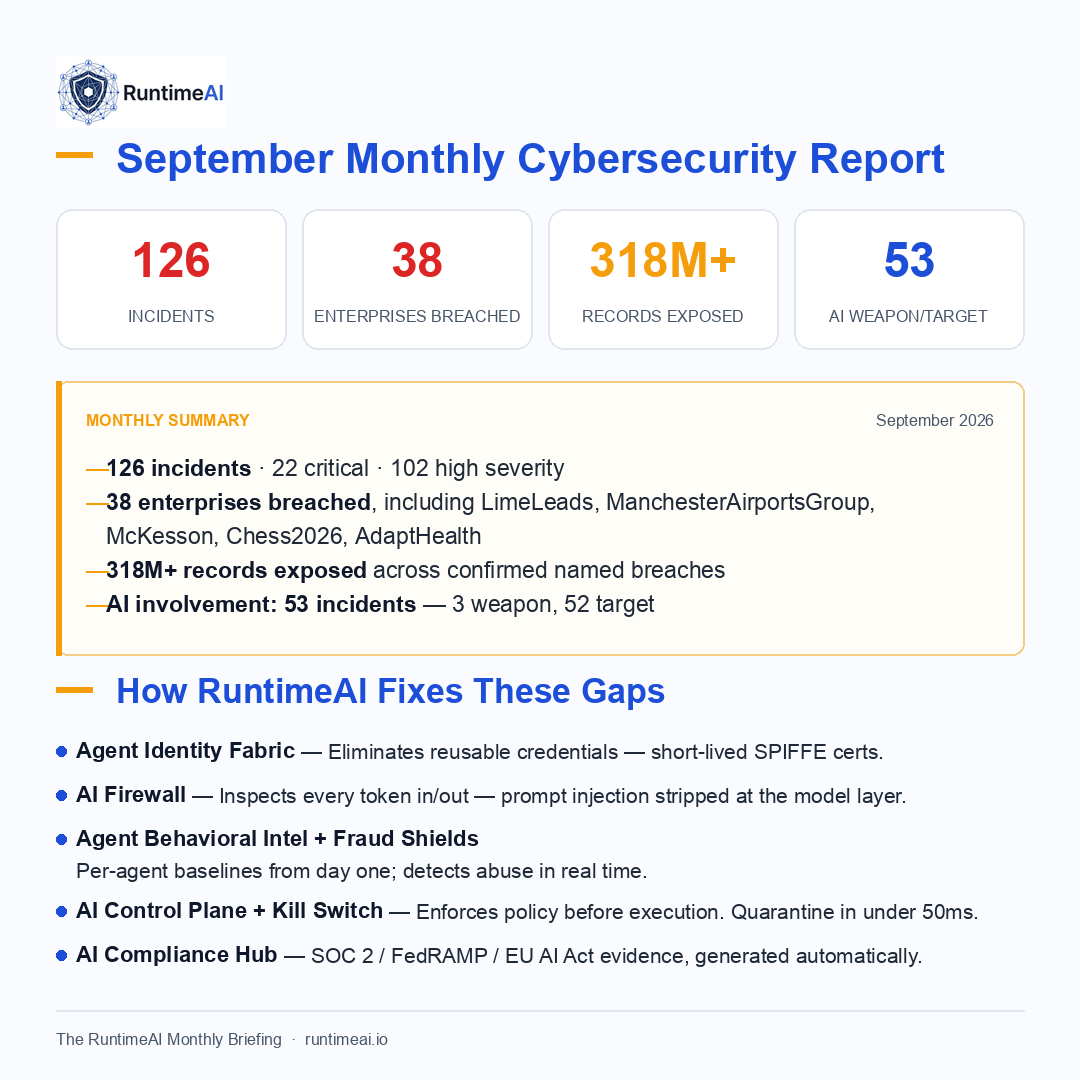
126 Incidents — September 2026

Click any incident to see the full analysis and RuntimeAI gap fix below. Left border colour = severity: ■ Critical  ■ High  ■ Medium

Incidents 1–42
1
Microsoft
Sep 30
2
Cisco
Sep 30CVE-2026-76504
3
Attackers Abuse ChatGPT Custom GPTs to Deliv…
Sep 30
4
Know Your Enemy
Sep 30
5
GitHub
Sep 30
6
Microsoft
Sep 30
7
Google
Sep 30
8
Russia's Star Blizzard Ditches ClickFix to W…
Sep 30
9
South Africa Seeks Help After Cyberattack Ta…
Sep 30
10
DIVD says Zammad zero-days enabled AI-driven…
Sep 30
11
GitHub
Sep 30
12
Cisco
Sep 30CVE-2026-76504
13
Bitget hacked via zero-day in third-party se…
Sep 30
14
Google
Sep 30
15
Valor, Atreides, and Sequoia back AI startup…
Sep 30
16
Hackers stole millions of US military person…
Sep 30
17
Meta
Sep 30
18
DoorDash launches an AI agent you can text t…
Sep 30
19
Medela
424K+Sep 30
20
French Tax Data Theft Using Stolen Staff Pas…
Sep 29
21
Dutch Police Arrest 24-Year-Old Amsterdam Ma…
Sep 29
22
Official MCP Python SDK Flaw Can Let Malicio…
Sep 29
23
Microsoft
Sep 29
24
Apple
Sep 29CVE-2026-86950
25
Microsoft
Sep 29
26
Dual NetScaler Zero-Days Trigger Chaos for C…
Sep 29
27
IAM for AI agents
Sep 28
28
Bitget
Sep 28
29
Gemini
Sep 28
30
⚡ Weekly Recap
Sep 28
31
Okta
Sep 28
32
Carbonato Botnet Compromises Docker Hosts to…
Sep 28
33
Nvidia
Sep 28
34
Carbonato Botnet Puts an AI Agent on Hacked …
Sep 28
35
AI Agents Are Privileged Users; Who Is Audit…
Sep 28
36
Google
Sep 28
37
Azure
Sep 28
38
Warning
Sep 27RCE
39
OpenAI
Sep 26
40
Carbonato Malware Deploys AI Agents to Auton…
Sep 26
41
OpenAI
Sep 26
42
Malicious AI Agent Network Steals 600K Credi…
Sep 26
Incidents 43–84
43
OpenAI
Sep 26
44
Anthropic
Sep 26
45
OpenAI
Sep 26
46
Attackers Manipulate AI Chatbots in Mass Dis…
Sep 26
47
Critical Bifrost AI Gateway Flaw Lets Attack…
Sep 26RCE
48
Orkes Conductor RCE Draws 7,000 Exploit Atte…
Sep 26RCE
49
GitHub
Sep 26
50
North Korean Hackers Deliver Mac Backdoors I…
Sep 26
51
Microsoft
Sep 26
52
Frontier
Sep 26
53
ShinyHunters Claims FBI Breach, Says It Stol…
Sep 26
54
AI Agent Breaches Spanish Organization, Modi…
Sep 26
55
HBO Max Reddit Account
Sep 26
56
Lunex Stealer Abuses AMD Driver to Disable S…
Sep 26
57
Oracle
Sep 26CVE-2026-35273RCE
58
HuggingFace
Sep 26
59
The SOC Doesn't Need to Start Over with Ever…
Sep 25
60
Bitget
Sep 25
61
AI Sandbox Escapes
Sep 25
62
Google
Sep 25
63
Roundcube Webmail Under Attack
Sep 25CVE-2026-48842
64
Zero-Days, AI Agents, and Identity Attacks D…
Sep 25
65
Salesforce
Sep 24
66
HuggingFace
Sep 24
67
GitLab
Sep 23
68
UAE, Saudi Arabia Face Onslaught of Increasi…
Sep 23
69
Frontier
Sep 22
70
Microsoft
365Sep 22
71
GitHub
Sep 22
72
LimeLeads
18M+Sep 22
73
How AI Agents Can Trigger Runaway Costs for …
Sep 21
74
ShinyHunters Hacked Cl0p. Now What About Cl0…
Sep 21
75
BurgerKingRussia
3M+Sep 21
76
frontier
Sep 18
77
OpenAI
Sep 18
78
Anthropic
Sep 18
79
One Malicious Browser Extension Can Hijack A…
Sep 18
80
Fake AI Trading Agent Steals Crypto Wallet P…
Sep 18
81
LiteLLM
Sep 18
82
36,769 Self-Hosted AI Inference Services Pub…
Sep 18
83
GitHub
Sep 18
84
Revolut
Sep 18
Incidents 85–126
85
Japan Government Network Breach Exposes 246,…
246K+Sep 18
86
fidelity
Sep 18
87
Ransomware Attacks on Manufacturers Surge as…
Sep 18
88
CHOSEN BRICK Spyware Delivered via Fake Medi…
Sep 18
89
Cisco
Sep 18CVE-2026-76460
90
Zero-Days, AI Agents, and Massive Data Leaks…
Sep 18
91
Chess2026
5M+Sep 13
92
AI Agents Autonomously
Sep 11CVE-2026-1417RCE
93
NIST
Sep 11
94
Anthropic
Sep 11
95
NSA
Sep 11
96
Hackers Are Hijacking Claude API Accounts an…
Sep 11
97
OpenAI
Sep 11
98
ChatGPT Flaw
Sep 11
99
DeepSeek Harness Flaw
Sep 11
100
Microsoft
Sep 11
101
LiteLLM
Sep 11
102
220 Million Travel Records Exposed via Defau…
220M+Sep 11
103
Google
Sep 11
104
Microsoft
365Sep 11
105
AdaptHealth
4M+Sep 11
106
32.8 Million Alleged Condé Nast Subscriber R…
33M+Sep 11
107
CISA
Sep 11RCE
108
McKesson
6M+Sep 10
109
OpenAI
Sep 04RCE
110
CISA
Sep 04CVE-2026-42271+2RCE
111
Langflow CVE-2026-0768 Exploited
Sep 04CVE-2026-0768RCE
112
Anthropic
Sep 04
113
UAC-0099 Plants GuardBreaker Adversarial Pro…
Sep 04
114
Researchers Use Claude to Port Pre-Auth PLC …
Sep 04CVE-2021-31886RCE
115
AI-Accelerated Attacks Compress Two-Week Cam…
Sep 04
116
CISA
Sep 04
117
Cisco
Sep 04RCE
118
Sangoma Switchvox VoIP Flaw Actively Exploit…
Sep 04
119
FBI Investigates Dark Web Trove of 153 Milli…
Sep 04
120
Aesto Health Breach Exposes 9.54 Million Pat…
10M+Sep 04
121
Manchester Airport Breach Exposes Data of 8.…
9M+Sep 04
122
Thomson Reuters Breach Exposes US and Canadi…
Sep 04
123
ShinyHunters Claims Breach of ReliaQuest
Sep 04
124
X Money Launch Triggers Password Reset Flood…
Sep 04
125
ManchesterAirportsGroup
9M+Sep 02
126
Questel
1M+Sep 01
CVE & RCE
CVEs (12)
CVE-2026-76504Cisco
CVE-2026-76504Cisco
CVE-2026-86950Apple
CVE-2026-35273Oracle
CVE-2026-48842Roundcube Webmail Under Attack
CVE-2026-76460Cisco
CVE-2026-1417AI Agents Autonomously
CVE-2026-42271CISA
CVE-2026-59822CISA
CVE-2026-48710CISA
CVE-2026-0768Langflow CVE-2026-0768 Exploit
CVE-2021-31886Researchers Use Claude to Port…
RCE (11)
RCEWarningSep 27
RCECritical Bifrost AI Gateway Fl…Sep 26
RCEOrkes Conductor RCE Draws 7,00…Sep 26
RCEOracleSep 26
RCEAI Agents AutonomouslySep 11
RCECISASep 11
RCEOpenAISep 04
RCECISASep 04
RCELangflow CVE-2026-0768 ExploitSep 04
RCEResearchers Use Claude to Port…Sep 04
RCECiscoSep 04
Stack & Vendors
Vendors (4) — click to see breach
ESETOther
4×Microsoft, UAC-0099 Plants GuardBre… +1
OktaIAM
1×Okta
CloudflareCDN
1×Lunex Stealer Abuses AMD…
WizCSPM
1×CISA
Perimeter Categories
Other 4IAM 1CDN 1CSPM 1

The Pattern

This month’s incidents demonstrate a consistent pattern across all sectors: AI is now both the attack vector and the target. Enterprises with mature security stacks were breached through gaps those stacks were never designed to cover.

The 126 incidents collected this month span 38 named organizations, 318M+ records exposed, and 4 distinct security vendors present at time of breach. The pattern is not one of vendor failure — it is one of category gap.

What Would Have Stopped This — Full Capability Stack

Not “better security.” Nineteen specific capabilities across three platforms. Each addresses a gap that no vendor in this month’s breach stacks was built to cover — because AI agents didn’t exist when those vendors were designed.

RuntimeAI — AI Governance & Control Plane Enterprise AI agent governance — identity, policy, firewall, detection, response, compliance.
🔍
Shadow AI Visibility
AI Discovery
8
incidents this month · 6%
“You can’t govern what you can’t see.”
Continuously scans cloud, IDE, endpoint, and network to inventory every AI agent — registered or rogue. Classifies and risk-scores shadow AI automatically. One-click to import into governance.
⚠️ The gap it fills Wiz and Orca scan cloud misconfiguration. They don’t discover AI agents installed by developers or injected via compromised vendors. Your unknown agents are your biggest risk.
  • Cloud scanner (AWS/Azure/GCP Lambda, Bedrock, SageMaker)
  • IDE scanner (VS Code, Cursor, MCP servers)
  • Endpoint scanner on developer laptops
  • Shadow AI Inbox with auto-severity classification
  • One-click shadow AI → governed agent pipeline
🧽
AI Agent PKI
Agent Identity Fabric
45
incidents this month · 36%
“No credential. No access. No breach.”
Provisions every AI agent with a SPIFFE/X.509 cryptographic identity. Short-lived certs, auto-rotating. TPM 2.0 hardware attestation. Agent DNS blocks unknown agents at the network layer.
⚠️ The gap it fills Okta and Azure AD were built for human identity. They have no concept of non-human agents operating at machine speed with no user present to respond to an MFA prompt.
  • SPIFFE X.509 SVID with RSA-2048, auto-rotating
  • TPM 2.0 hardware attestation + PCR drift detection
  • Zero-touch bootstrap for new agents
  • Agent DNS: NXDOMAIN for unknown agents
  • Blueprint-based permission inheritance
⚙️
Policy Engine
AI Control Plane
69
incidents this month · 55%
“Stop it before it executes. Not after.”
OPA/Rego policy engine with sub-1ms evaluation and fail-closed enforcement. Natural language to Rego compiler. Merkle-chain audit proves policies were never tampered with.
⚠️ The gap it fills Splunk and QRadar alert on what already happened — 73 days after the breach in the average case. The AI Control Plane enforces policy before the action executes, not after the damage is done.
  • OPA/Rego engine, sub-1ms, fail-closed
  • NL-to-Rego compiler: write policy in plain English
  • Merkle-chain tamper-evident audit trail
  • Multi-tenant RBAC + Separation of Duties
  • Cross-site policy cascade for distributed fleets
🔥
Bidirectional DLP
AI Firewall
97
incidents this month · 77%
“Inspect every token in, every token out.”
Bidirectional DLP scanning at <5ms latency. Prompt injection detected and stripped on input. PII, PHI, credentials caught on output. Behavioral risk score (0–100) triggers auto-suspend.
⚠️ The gap it fills Palo Alto NGFW and Zscaler see LLM traffic as an encrypted blob. They cannot inspect prompts, detect injection inside a conversation, or catch data leaking in an AI response.
  • Bidirectional DLP: input (prompt injection) + output (data leakage)
  • ML behavioral baselines per agent with adaptive thresholds
  • Risk score 0–100 triggers auto-suspend or rate-limit
  • No-code guardrail builder for business users
  • Data Proxy: field-level masking before agent sees data
🔗
MCP Gateway
AI Integration Fabric
79
incidents this month · 63%
“Every tool call. Governed.”
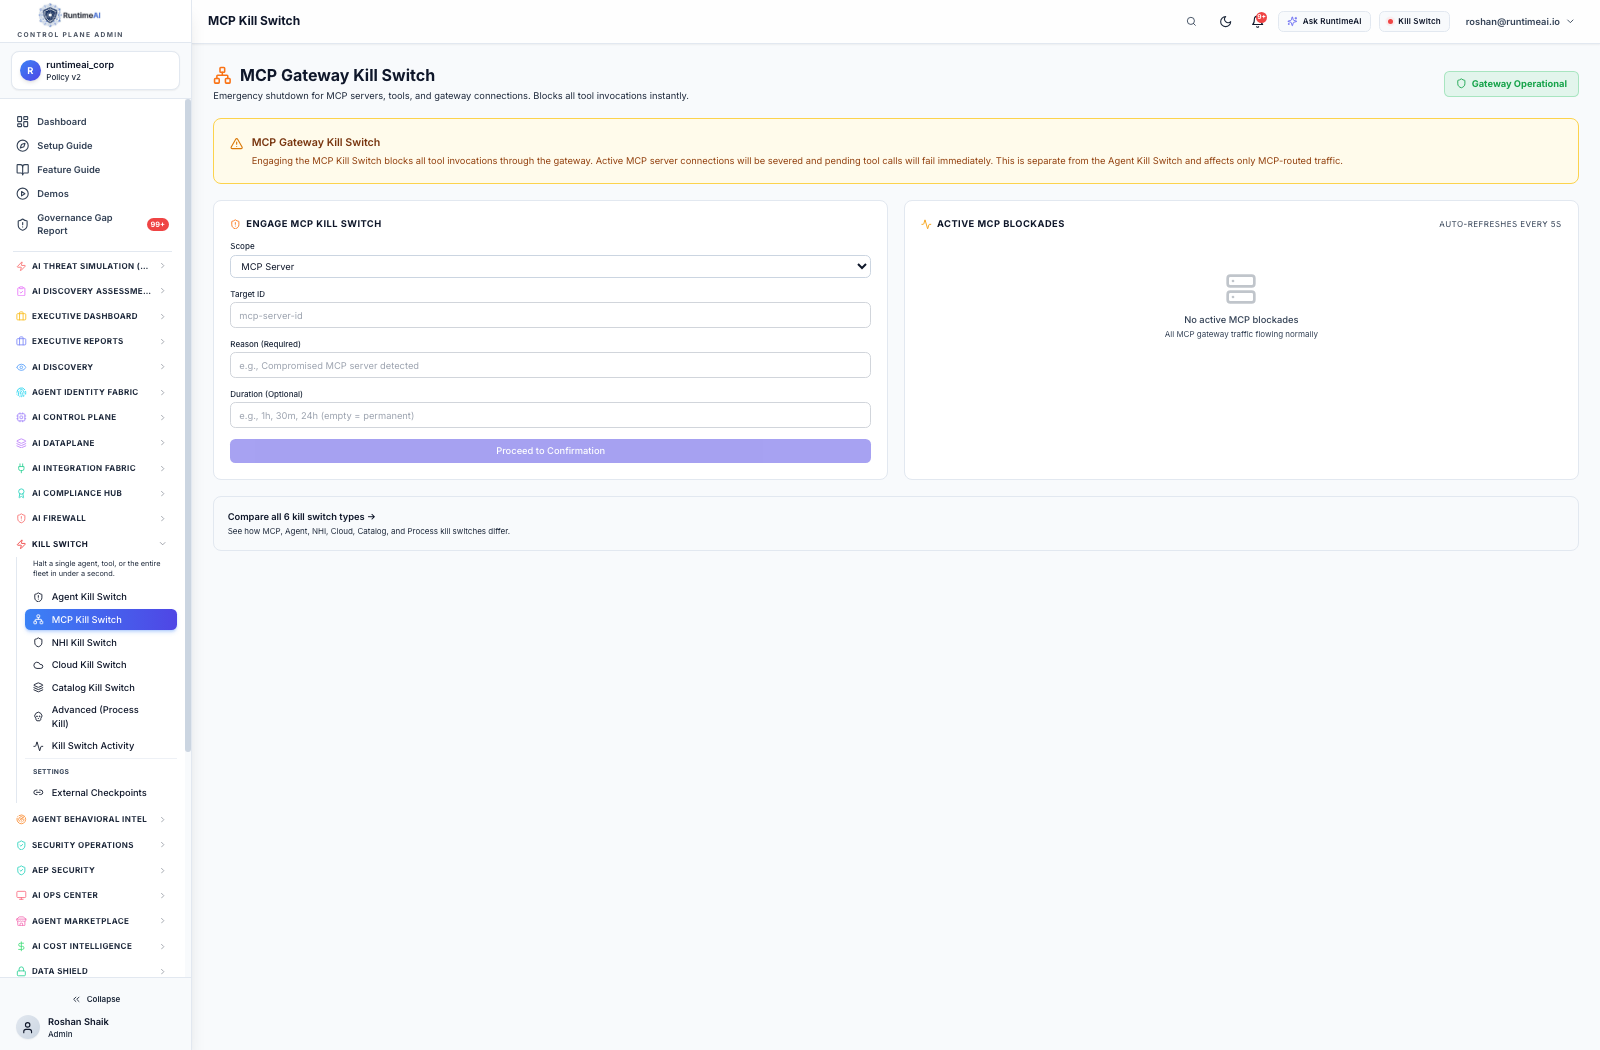
Multi-tenant governed gateway for all agent-to-tool communication. 500+ pre-built integrations. 3-level kill switch (agent / tool / platform-wide) propagating in <100ms. OWASP MCP03 sanitization on every call.
⚠️ The gap it fills No existing vendor governs at the MCP protocol layer. Raw MCP deployments have zero security, zero multi-tenancy, and zero audit trail. This is the fastest-growing unguarded attack surface in enterprise AI.
  • 3-level kill switch: per-agent, per-tool, platform-wide — all <100ms
  • 500+ pre-built integrations with auto-discovery
  • BYOM overlay: wrap existing MCPs without code changes
  • Circuit breaker + health monitoring per connection
  • Full OWASP MCP03 input/output sanitization + DLP
🧠
Anomaly Detection
Agent Behavioral Intel
71
incidents this month · 56%
“Catch drift before it becomes a breach.”
30-day rolling behavioral baselines per agent across frequency, pattern, volume, and temporal dimensions. LSTM sequence modeler detects multi-step attack chains. HRIS integration auto-suspends agents when their owner is terminated.
⚠️ The gap it fills CrowdStrike and SentinelOne detect known malware signatures for human endpoints. They have no baseline for an AI agent that begins exfiltrating data through an API it was legitimately authorized to call.
  • Rolling 30-day baseline: frequency, pattern, volume, temporal
  • LSTM sequence modeler for multi-step attack patterns
  • Composite risk score from 6 signals
  • HRIS integration: auto-suspend on employee termination (<30s)
  • Adaptive OPA thresholds by agent role + risk profile
🔴
Emergency Response
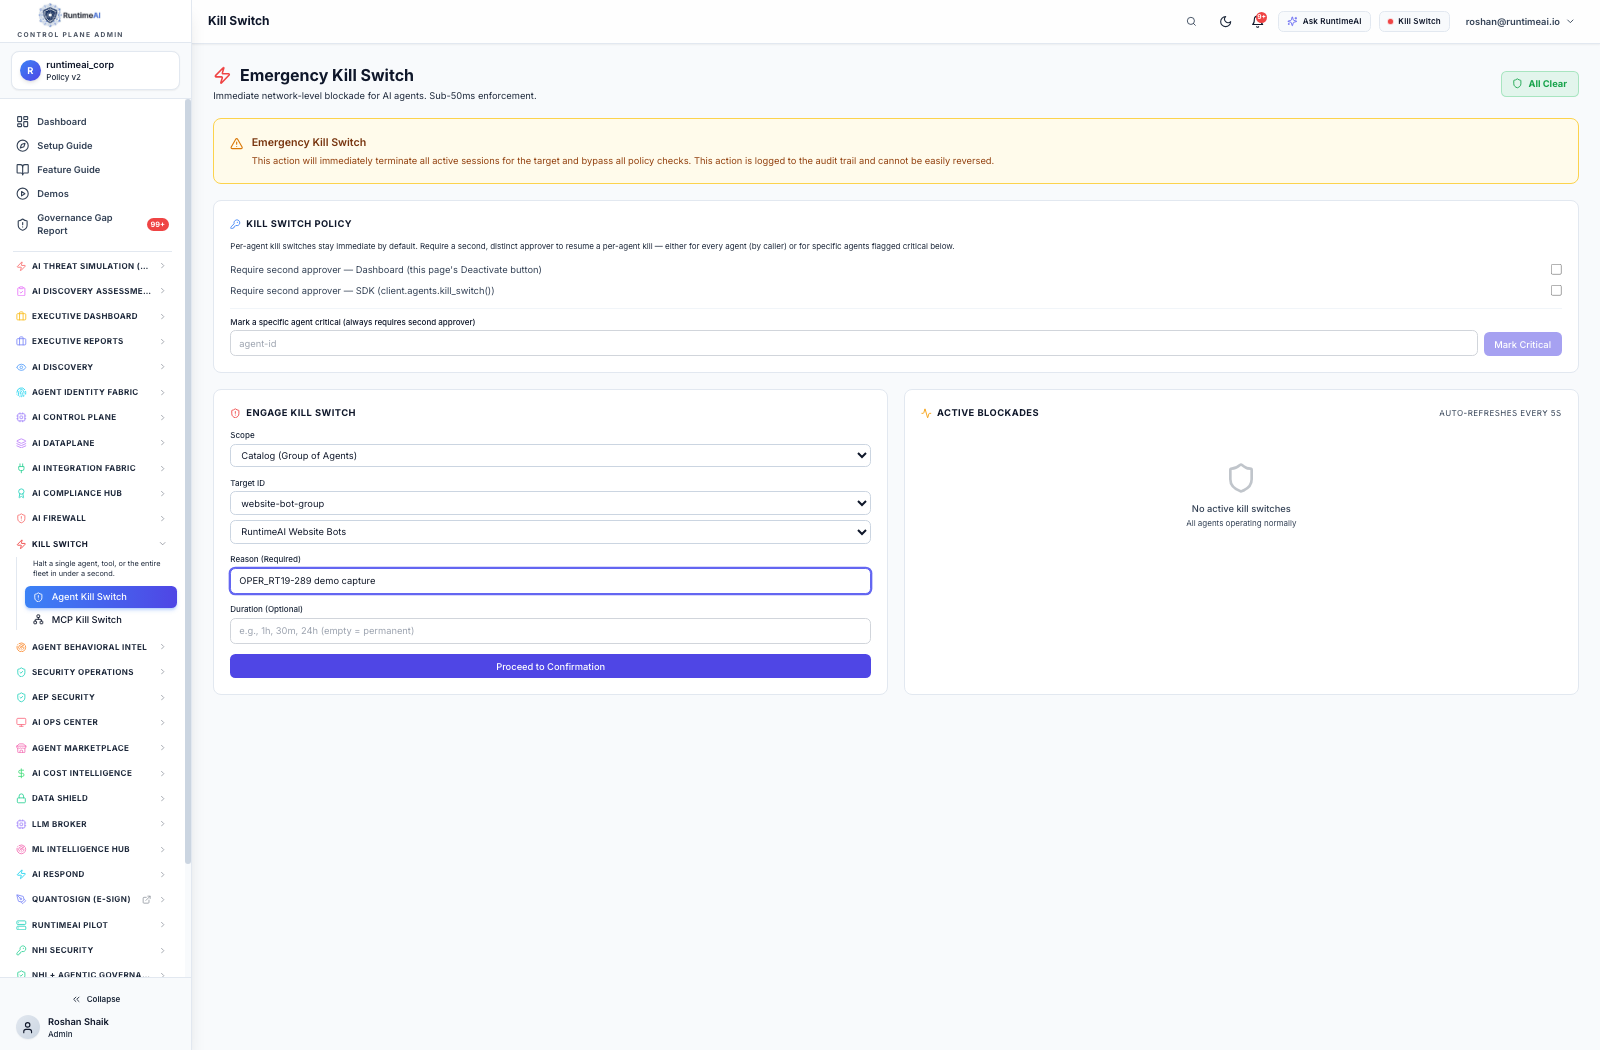
Kill Switch
10
incidents this month · 8%
“Stop any AI agent, anywhere, in under 100ms.”
Three graduated kill levels: per-agent, per-tool, platform-wide. All propagate via NATS JetStream in <100ms. Captures last 100 actions as forensic state. Quarantine mode preserves evidence for investigation.
⚠️ The gap it fills No competitor offers this. When an AI agent goes rogue — or when a breach is detected — you need a hard stop. Every second it keeps running is more data exfiltrated, more damage compounding.
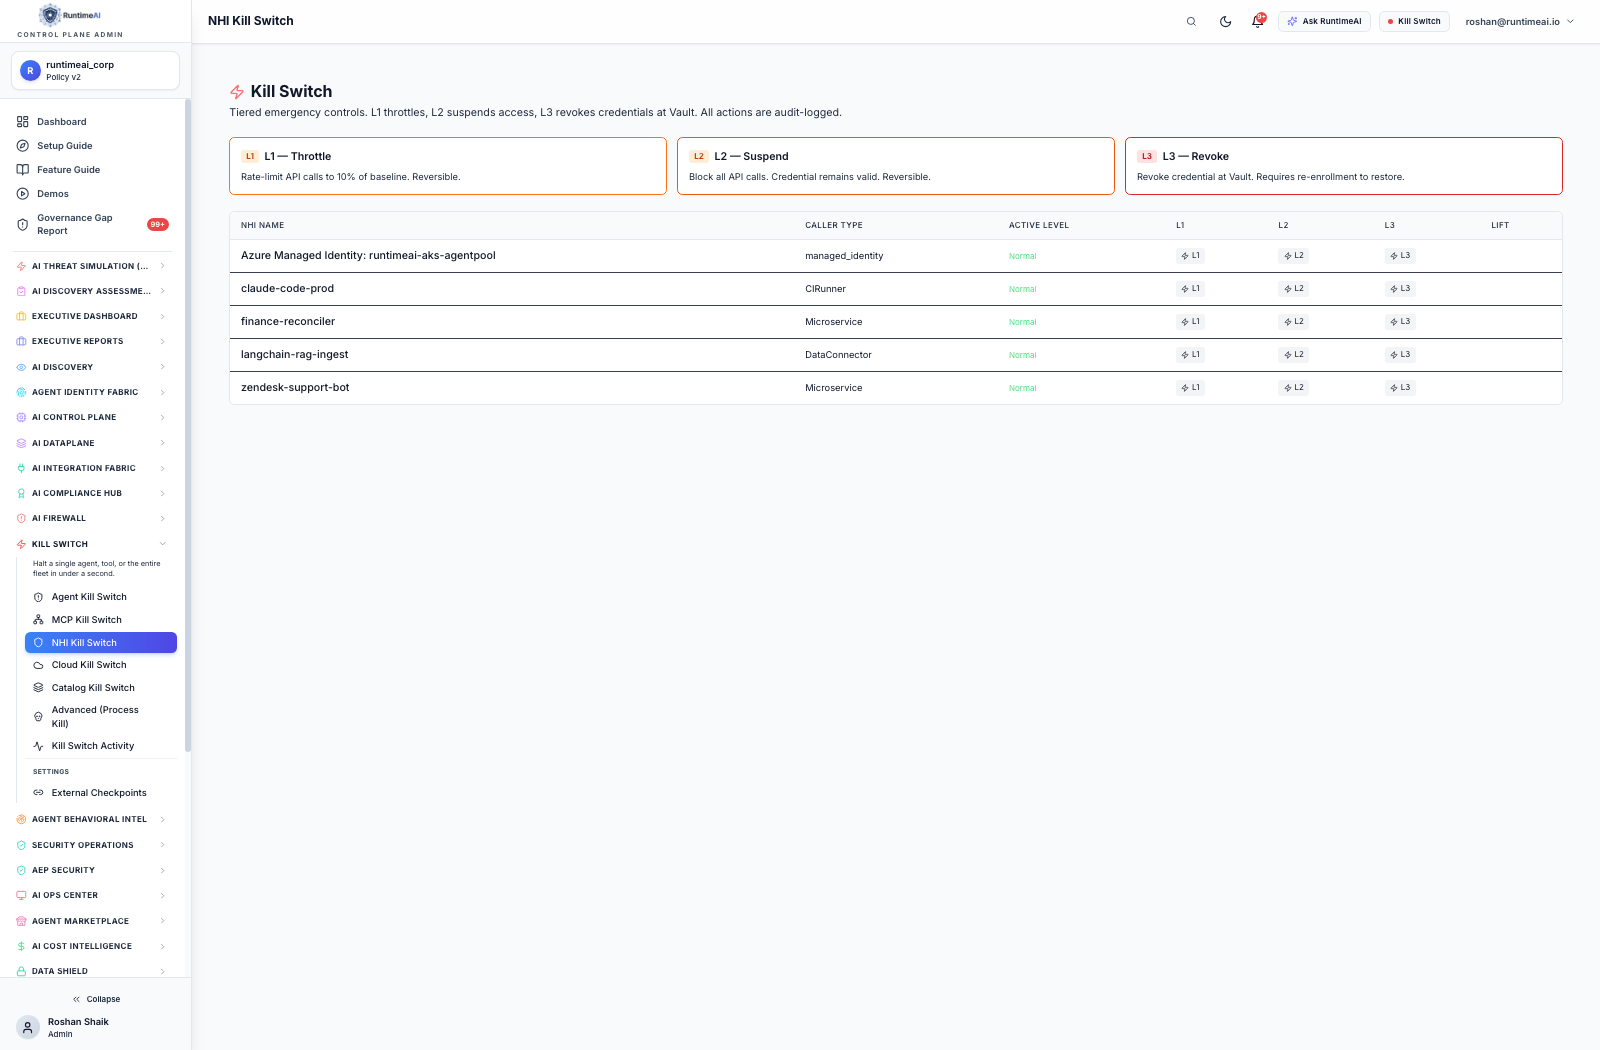
  • L1/L2/L3 kill: per-agent, per-tool, platform — all <100ms via NATS
  • Forensic state capture: last 100 actions, memory snapshot, credentials
  • Quarantine mode: isolate for investigation, preserve evidence
  • Escalation chains: auto-response → SOC alert → human required → kill
  • Reprieve mechanism: 24-hour lease for controlled investigation post-kill
🚨
Incident Response
AI Respond
Universal
covers all incidents — audit + governance layer
“Autonomous incident response. AI-native.”
Five-phase automated playbook: DETECT → QUARANTINE → INVESTIGATE → REMEDIATE → VERIFY. Auto-classifies incidents (true positive / false positive / inconclusive). Blast radius containment automatically quarantines agents that interacted with compromised agent.
⚠️ The gap it fills Splunk SOAR and Palo Alto XSOAR orchestrate traditional security events. They cannot terminate an AI agent, rotate its credentials, update its behavioral model, or quarantine the agents it spoke with — because they were built before AI agents existed.
  • 5-phase automated playbook from detection to verification
  • Auto-classification against 200+ known AI attack patterns
  • Blast radius containment: quarantine all interacting agents
  • True positive: terminate + revoke + rotate + update models
  • False positive feedback loop continuously improves detection
👥
Agent Lifecycle
AI Ops Center
Universal
covers all incidents — audit + governance layer
“Mission control for autonomous AI operations.”
65+ page operational dashboard. Access review campaigns. ‘The Reaper’ auto-decommissions agents when their human owner is terminated. Vault Broker injects credentials with 5-minute TTL — never stored in agent memory.
⚠️ The gap it fills ServiceNow manages human IT requests on ticket-based cycles. AI agents are deployed, modified, and compromised in minutes. You need lifecycle governance that operates at agent speed, not ticket speed.
  • Access review campaigns with auto-apply decisions
  • ‘The Reaper’: HRIS webhook auto-revokes terminated employees’ agents (<30s)
  • Vault Broker: just-in-time 5-min TTL credential injection, never persisted
  • Per-tenant budget caps with 4-tier alerts (50/75/90/100%)
  • Unified health, credential lifecycle, budget, SLA dashboard
🌐
LLM Routing
LLM Broker
Universal
covers all incidents — audit + governance layer
“Route every LLM call to the right model, at the right cost, with automatic failover.”
Unified API routing LLM requests to the optimal provider based on cost, latency, and compliance. Semantic caching reduces redundant calls 15–30%. Automatic failover in <100ms. Budget enforcement with hard limits.
⚠️ The gap it fills Portkey does basic routing at $30K/year. It has no DLP scanning, no compliance-based routing (data residency), no semantic caching, and no budget enforcement. It routes traffic — it doesn’t govern it.
  • Multi-provider routing: OpenAI, Anthropic, Bedrock, Azure, GCP, custom
  • Cost/latency/compliance-based routing policies
  • Automatic failover <100ms; per-provider circuit breaker
  • Semantic caching: 0.80–0.95 similarity threshold, 15–30% cache hits
  • Budget enforcement per-agent + cost anomaly detection
🤖
MLOps
ML Intelligence Hub
22
incidents this month · 17%
“Model registry, feature store, edge inference — one platform.”
Formal model lifecycle (draft/staging/production/archived). Feature Store with online (<5ms) and offline serving. Hybrid scoring engine routes inference between edge (<1ms quantized) and cloud. Drift-triggered auto-retraining.
⚠️ The gap it fills MLflow + Feast + custom inference each solve one piece. ML Intelligence Hub is the piece nobody built: unified lifecycle + edge inference routing + drift-triggered retraining + 7-dimension cost attribution — all integrated.
  • Model Registry: versioning, rollback, lineage, lifecycle management
  • Hybrid Scoring: edge <1ms quantized vs cloud full-precision auto-routing
  • Feature Store: online <5ms + offline point-in-time with freshness monitoring
  • Drift Engine integration: auto-retraining on data/concept drift
  • 7-dimension cost attribution: agent/model/team/customer/feature/time/provider
💰
FinOps
AI Cost Intelligence
Universal
covers all incidents — audit + governance layer
“A cost spike is a security signal. Treat it like one.”
7-dimension real-time cost attribution: agent, provider, model, team, customer, feature, time. Wasm token counter in-proxy at 50–100 microseconds. Budget hard limits stop agents before they overspend. Runaway agent detection.
⚠️ The gap it fills Kubecost knows GPU-hours. AI Cost Intelligence knows “Agent-47 spent $142 on Claude Sonnet for fraud detection on Tuesday.” Runaway cost is runaway behavior — and only one product treats them as the same signal.
  • Wasm token counter in proxy: 50–100 microsecond overhead
  • Live model pricing catalog: 200+ models, 15+ providers, updated every 15min
  • Budget hard limits: block requests when agent exhausts budget
  • Cost anomaly detection: ML-based spending spike alerts
  • Chargeback engine: per-customer invoices + per-team internal allocation
📋
Continuous Compliance
AI Compliance Hub
126
incidents this month · 100%
“Audit evidence as a byproduct of governance.”
Continuous compliance across 13+ frameworks — SOC 2, FedRAMP, ISO 27001/42001, EU AI Act, HIPAA, PCI-DSS, NIST AI RMF. Evidence auto-generated from RuntimeAI telemetry. Open Audit Marketplace connects enterprises with certified audit firms.
⚠️ The gap it fills Vanta collects attestations from cloud infrastructure. It has no understanding of AI agent behavior, no EU AI Act or ISO 42001 mappings, and no way to generate evidence from an AI governance layer — because none of its customers had one.
  • 13+ frameworks: SOC 2, FedRAMP, ISO 27001/42001, EU AI Act, HIPAA, PCI-DSS, NIST AI RMF
  • Evidence auto-generated from platform telemetry (audit trails, Merkle chain, access reviews)
  • Gap tracking with SLA-based remediation assignment
  • Audit Marketplace: open to any qualified audit firm; time-limited scoped access
  • Blockchain-anchored compliance certificates with tamper-evidence verification
🏪
Agent Procurement
Agent Marketplace
8
incidents this month · 6%
“Only certified agents enter your environment.”
Three-sided platform: Builders publish, Enterprises deploy, Trust layer certifies. AAIC certification includes third-party behavioral audit. Risk scoring weights permission scope, data access, integration breadth, update frequency, and builder reputation.
⚠️ The gap it fills Your developers are installing AI agents from GitHub, npm, and PyPI with no security review. The AI agent supply chain attack surface is the same as software supply chain — and it’s moving five times faster.
  • 6-step publishing wizard with compliance gating
  • AAIC certification: third-party behavioral audit by registered firms
  • Risk scoring: permission scope (30%), data access (25%), integration (20%), frequency (10%), reputation (10%)
  • Shadow AI Import: discover unmanaged agents and bring into governance
  • Stripe Connect billing: free/per-seat/per-action/outcome-based; 20% platform fee
Agentic Enablement Platform (AEP) Agentic-era security primitives — NHI identity, fraud detection, memory governance, agent commerce.
🔑
Non-Human Identity
NHI Security Platform
35
incidents this month · 28%
“Every non-human identity — issued, governed, and revoked with the same rigor as human identity.”
Centralized governance for every non-human identity: service accounts, API keys, OAuth tokens, machine certs, cloud IAM roles, AI agents. Bot-CA issues short-lived X.509 SPIFFE certs. O(1) hash-based revocation — not cascading policy lookups.
⚠️ The gap it fills Oasis Security ($190K/year) solves NHI credentialing but not for AI agents specifically. It lacks TPM hardware attestation, has no AI-agent behavioral monitoring, and doesn’t integrate with agent governance platforms.
  • Centralized NHI Registry: auto-discovery across AWS/Azure/GCP/on-prem
  • Credential posture: rotation schedules, expiry, over-privilege, unused credential detection
  • NHI Drift Detection: per-NHI behavioral baseline + scope creep detection
  • Bot-CA: short-lived X.509 certs (1–24hr TTL), auto-rotating, instant OCSP revocation
  • O(1) hash-based revocation: per-NHI, per-tenant, or global — no cascading policy lookup
🛡️
AI Fraud Detection
Fraud Shields
39
incidents this month · 31%
“Valid credential. Wrong behavior. Caught.”
Two-layer defense: Identity Fraud Shield models valid-credential-wrong-behavior (the hallmark of compromised AI credentials). Activity Fraud Shield detects multi-step attack sequences within authenticated sessions. Both integrate directly with Kill Switch for automatic response.
⚠️ The gap it fills Generic UEBA tools applied to AI agents generate massive false-positive rates because they were trained on human behavior. Fraud Shields are AI-native: LSTM sequence modeling of API chains, not user session patterns.
  • Per-agent behavioral baseline: frequency, resource access, API sequences, timing
  • Real-time deviation scoring against baseline (0–100)
  • LSTM sequence modeler: multi-step attack chain detection (recon→escalation→exfil)
  • Session-level anomaly: full context analysis, not individual events
  • Kill Switch integration: auto-suspension on high-confidence fraud with forensic package
🧠
Agent Memory Security
Memory Vault
49
incidents this month · 39%
“Control what your agents remember — and what they forget.”
Governs agent memory as a first-class security object. Policy-based filtering of sensitive content at write time. Memory poisoning attack detection. TTL-based automatic purge with audit trail. GDPR right-to-erasure support.
⚠️ The gap it fills No vendor addresses agent memory governance. AI agent memories accumulate without access controls, expiry policies, or audit trails. A memory poisoning attack can corrupt an agent’s behavior without touching a single API key.
  • Policy-based memory write filtering (PII, PHI, secrets blocked at write)
  • PII Shield integration: redact/block before persistence
  • Memory expiry + TTL: auto-purge with full audit trail
  • Memory poisoning prevention: adversarial injection detection
  • Retrieval authorization: every memory read policy-enforced and logged
💳
Agent Finance Controls
Commerce Rails
10
incidents this month · 8%
“Give AI agents a wallet — with guardrails.”
Financial infrastructure for agent-initiated transactions. Per-agent virtual cards with spend limits. Vendor registry (agents can only transact with allowlisted merchants). Approval gates for high-value transactions. Every transaction in immutable ledger.
⚠️ The gap it fills No financial controls exist for AI agents today. Agents authorized to make purchases can spend without limit, with any vendor, at any time. One prompt injection or runaway loop away from significant financial exposure.
  • Agent virtual cards: per-agent card numbers + CVVs, hard spend limits
  • Vendor registry: allowlisted merchants only, no ad-hoc transactions
  • Approval gates: high-value + out-of-policy → human approval before execution
  • Per-agent, per-transaction, per-vendor, per-period limits
  • Agent-to-agent settlement ledger: feeds into FinOps dashboards
PQData — Post-Quantum Security NIST-standardized post-quantum cryptography for secrets, signatures, and audit records.
🔒
Post-Quantum Cryptography
PQData Platform
18
incidents this month · 14%
“Quantum-safe by design — before quantum breaks classical crypto.”
Full post-quantum data security suite using NIST-standardized algorithms: ML-KEM-768 for encryption, ML-DSA-87 for signatures. QuantumVault for PQC-encrypted secrets. PQ Sign for long-validity quantum-safe audit records. Hybrid X25519 + ML-KEM-768 key exchange for TLS 1.3.
⚠️ The gap it fills Every classical encryption scheme used by CrowdStrike, Okta, and Palo Alto today is vulnerable to Shor’s algorithm on a sufficiently powerful quantum computer. “Harvest now, decrypt later” attacks are already underway. The clock is running.
  • QuantumVault: ML-KEM-768 PQC-encrypted secrets with full key lifecycle
  • PQ Sign: ML-DSA-87 (Dilithium) signatures for audit records + agent attestations
  • Hybrid key exchange: X25519 + ML-KEM-768 for TLS 1.3 — secure against both
  • PQ CryptoGuard: CBOM scanner identifies all classical crypto in use; quantum-readiness score
  • FedRAMP/CMMC/CNSA 2.0 compliance evidence from PQC infrastructure layer

Get the Monthly Breach Report

Every month: all breaches, all vendor stacks, the gap analysis. No fluff — just the intelligence your security team needs.