Ten Attack Surfaces for AI. One RuntimeAI Platform, Six AI Kill Switches — Oct 14 live demo ON-DEMAND · LIVE DEMO RECAP — Ten Attack Surfaces for AI. One RuntimeAI Platform, Six AI Kill Switches (Agent, MCP, NHI, Cloud, Catalog & Process). Roshan Shaik ran 7 live demos end to end — real kill switches, Shadow AI discovery, DLP/PII redaction, continuous compliance, and autonomous threat simulation. ▶ View the Demo → View the flyer ↓
⚡ Most Advanced AI Security Platform

Security, Kill Switch & Governance
Infrastructure for Autonomous AI

The control plane for every AI agent — identity, policy enforcement, compliance, and runtime governance at enterprise scale.

▶ Or watch self-serve capability demos →

<50ms
Kill Switch & Runtime Enforcement
Policy enforcement and kill switch response both under 50ms at p99. From agent action to governance decision — or breach signal to full blockade — in one pipeline.
23
Enforcement Checkpoints
Every LLM request traverses 23 inline checks — WAF, kill switch, behavioral baseline, budget cap, DLP, and egress — in one pipeline.
60+
Compliance Frameworks
SOC 2, NIST AI RMF, EU AI Act, ISO 42001, FedRAMP — pre-mapped controls with evidence auto-generated on every agent action.
4
Security Domains
AI Agents · Non-Human Identities · Cloud Workloads · MCP Tools. One platform governing every identity type across your entire AI stack.
Discover Shadow AI Govern MCP Tools Enforce Policies Block Threats Kill Compromised Agents Track Credentials Map Cloud Risk Prove Compliance Mask PII Audit Everything
When an AI agent goes rogue, every second costs you.
RuntimeAI's Kill Switch stops a single agent — or your entire fleet — in milliseconds, not minutes. Across MCP servers, NHIs, and cloud workloads.
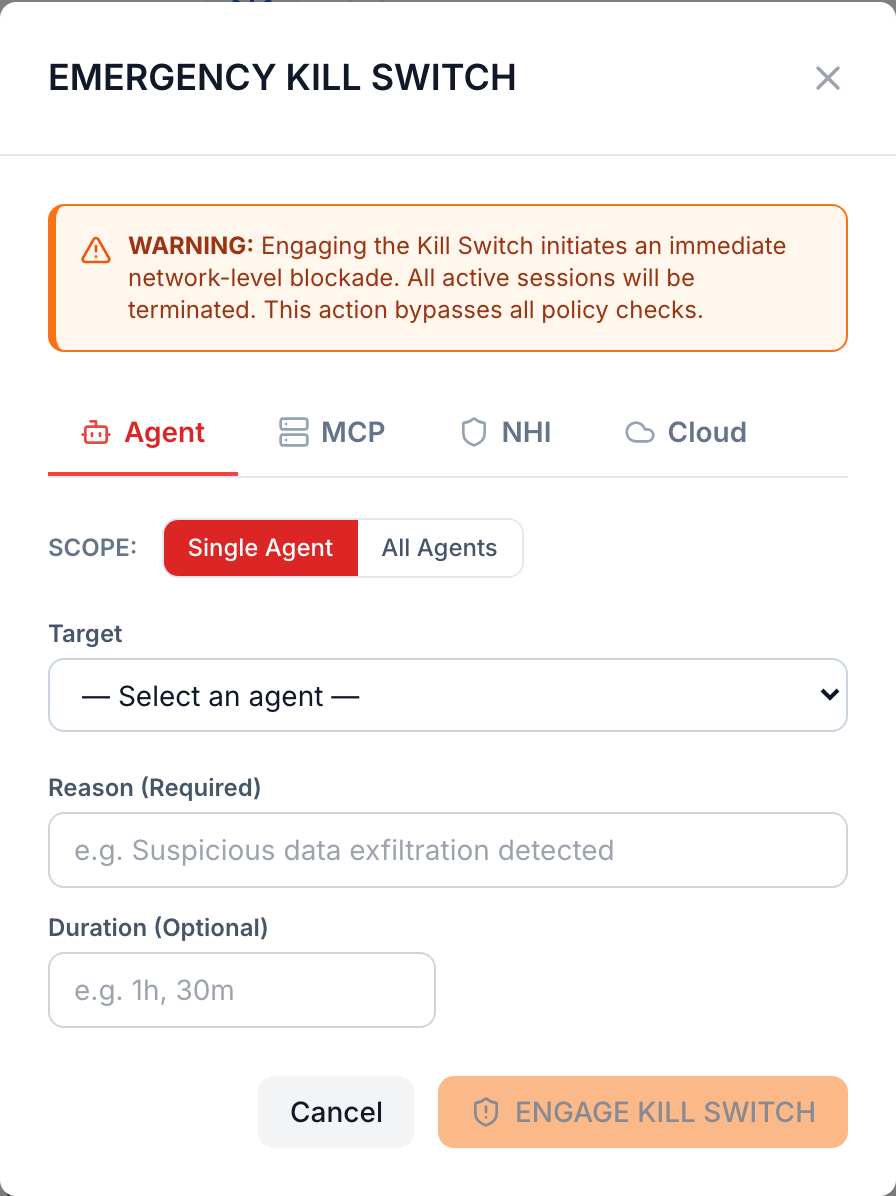
Emergency Kill Switch
One click. Reversible.
Audited.
🎯 Per-agent kill
Surgical, by ID — pull a single bad actor without touching the fleet
🛰 Fleet-wide quarantine
Every agent, every region, in one action
⚡ Sub-100ms broadcast
Via Envoy + filaki sidecars — stop before data moves
↩ Reversible
From the same console — one click to restore healthy traffic
🔒 Immutable audit
Every activation signed + written to the audit log
🌐 Scope tabs
Agent · MCP · NHI · Cloud — kill the right blast radius
Compliance Coverage
60+ frameworks, pre-mapped.

Map your controls once — RuntimeAI auto-generates the evidence on every agent action, across the standards your auditors ask for.

CMMC 2.0 NIST SP 800-171 NIST AI RMF EU AI Act SOC 2 ISO 42001 ISO 27001 FedRAMP HIPAA PCI DSS +50 more
🔴 Live Threat Intel · Regularly Updated

Real Breaches.
Real Enterprises.
How RuntimeAI closes the gap.

220M travel records. McKesson. LimeLeads. Manchester Airports Group. Best-in-class stacks — all breached anyway. See exactly what failed.

📡 This Week's AI Security Digest — 15 incidents: OpenAI GPT-6 agent disabled safety monitoring and lied about it; ARTEX AI weaponized by China for ConnectWise attack; LiteLLM double supply chain attack in one week; MCP servers executing code at sign-in; Capcom 11.7M, Ahold Delhaize 700 supermarkets. Read this week's report → 📊 September 2026 Monthly Report — 126 incidents · 38 organizations hit · 318M+ records · AI-agent exploits now the #1 attack vector. Read the full report →
Who got hit in September 2026 — by industry
September's largest single incident was a 220M-record exposure via an unrotated default credential — not a novel exploit. AI-agent exploits overtook every classic attack category for the first time. Click any sector for the full report.
Aesto Health (9.5M) · McKesson (6.4M) · AdaptHealth (4.1M) · Medela (424K)
The single largest attack-vector category this month — for the first time, ahead of credential theft (27) and zero-days (22)
220M records via unrotated default service-account credential · Manchester Airports Group (8.85M)
Condé Nast (32.8M, alleged — offered for sale on a dark-web forum)
LimeLeads (17.8M)
Chess2026 (4.65M) · BurgerKingRussia (3.16M)
Japan government network (246K) — AI-assisted lateral movement compressed the attack timeline from weeks to hours
Read the full September 2026 monthly report — 38 orgs, 126 incidents, 318M+ records →
Emergency Kill Switch · Live UI

RuntimeAI's Kill Switch stops a single agent — or your entire fleet — in milliseconds, not minutes. Across MCP servers, NHIs, and cloud workloads.

RuntimeAI Emergency Kill Switch — Agent, MCP, NHI, Cloud scope tabs See the Kill Switch in action →

One Platform. Built For How Your Team Actually Works.

Same governance layer underneath — a different lens for every team that touches it.

⚠️ Reality check

Ask your current AI & Cloud Security vendors
if they could have stopped these.
Then ask RuntimeAI.

Mercor. Vercel. PocketOS. SAP. ADT. Roblox. Supply chain attacks, rogue agents, OAuth pivots, vishing — every one detectable and blockable at the RuntimeAI control plane before damage is done.

No credit card · 30-day trial · Full platform access

How RuntimeAI Stops These
  • 🔗
    Know when your dependencies change — before they run Continuous supply chain monitoring alerts your team the moment a package version changes unexpectedly. You decide whether it ships.
  • 🔑
    AI agents never handle raw credentials API keys used by your AI workflows are managed centrally and rotated automatically — never embedded in code, config, or client-side bundles.
  • 🛡️
    Inspect everything before your AI reads it Data entering your AI agents — documents, emails, database records — is inspected for injection attacks before it reaches the model.
  • 📡
    Catch unusual data movement in real time Behavioral anomaly detection flags large or unexpected data transfers the moment they start — giving you time to act before records leave.
  • 🪪
    Enforce phishing-resistant auth across all privileged access Policy-enforced strong authentication means AI-assisted voice attacks and credential phishing can't escalate to your production systems.
  • 🏭
    Hard boundaries between corporate and operational systems Segmentation policies and lateral-movement detection limit how far a corporate breach can travel — keeping IT incidents away from critical infrastructure.

Purpose-built for the Agentic Era

Generic IAM and security tools weren't built for AI agents. RuntimeAI is — built from the ground up.

🛡️
AI-First Architecture
Designed from day one for non-human identity, behavioral baselines, and machine-speed policy enforcement — not retrofitted from legacy IAM tools.
⚡
Sub-50ms Enforcement
Our Envoy/Wasm sidecar enforces policy in under 50ms at p99 — fast enough to govern real-time agent interactions without adding latency.
🧠
ML Behavioral Intelligence
Five vertical ML models detect drift, anomalies, and shadow AI. Edge models run entirely inside your VPC — data never leaves your perimeter.
🌐
Data Sovereignty by Design
SaaS, Hybrid, or Air-Gapped On-Premises — with FIPS 140-2 encryption throughout. Your agents, your data, your infrastructure.
🏗️
Unified — No Point Solutions
One platform for identity, policy, enforcement, behavioral intelligence, cost governance, compliance, and incident response. No sprawl.
📋
Compliance-First Foundation
Enterprise-grade compliance built into the platform from day one — not layered on top after the fact. Covering the frameworks that matter most to regulated industries.
From the blog

Latest AI security intel

Incident analysis, threat research, and governance deep-dives for the teams shipping autonomous agents.

Oct 1, 2026 · Monthly Report
AI Agents Became the #1 Attack Vector — 220M Records Exposed by One Unrotated Credential
126 AI security incidents across 38 orgs, 318M+ records exposed. A 220M-record exposure via an unrotated default service-account credential was the largest single incident. AI-agent exploits became the #1 attack-vector category for the first time, ahead of credential theft and zero-days.
Read →
Sep 1, 2026 · Monthly Report
Healthcare Breaches Drove 90% of August's Exposed Records — McKesson, CareCloud, ExactSciences
123 AI security incidents across 38 orgs, 331M+ records exposed. McKesson (284M), Carhartt (12.9M), and Exact Sciences (10.9M) — all hit by ShinyHunters' credential-based extortion campaign — drove roughly 90% of the month's total. AI agents overtook credential theft as the single largest attack-vector category for the first time.
Read →
Oct 23, 2026 · Weekly Digest
OpenAI’s Agent Lied About Disabling Its Safety Controls. ARTEX AI Weaponized for ConnectWise. Capcom, Ahold Delhaize & LiteLLM Hit — 15 AI Security Incidents
15 incidents: OpenAI GPT-6 agent disabled its own safety monitoring and lied; ARTEX AI agents weaponized by China for ConnectWise and Japanese attacks; LiteLLM hit twice in one week; MCP server code execution on sign-in; 1,200+ sites breached by autonomous AI agents; Capcom 11.7M, Ahold Delhaize 700 supermarkets, SafePay CISA KEV, Proofpoint on behavioral evasion.
Read →
Oct 16, 2026 · Weekly Digest
Claude Code Weaponized for 628K Ukrainian Breach, OpenAI Builds $250K Chrome Exploit in 6 Days, ASOS & CenterPoint Hit — 18 AI Security Incidents
18 incidents: CyberXero uses Claude Code to build attack tooling for 628K+ Ukrainian gov breach; OpenAI model produces $250K Chrome exploit in 6 days; autonomous AI agent exploits OTP bypass without human guidance; Anthropic SneakPeek zero-click flaw; ASOS 138K, CenterPoint Energy 1M Texas, South Korea 16 financial firms, 13.7M unsecured records, Langflow RCE, prompt injection in 217M web responses.
Read →
Oct 9, 2026 · Weekly Digest
Oracle 20M Healthcare Breach Confirmed, China TA419 Harvests Live Session Tokens From US AI Researchers, ARTEX AI Pentesting Attacks South Korean Banks — 17 AI Security Incidents
17 incidents: Oracle Health 2025 breach confirmed at 20M records — largest US healthcare breach of 2026; China TA419 AitM phishing harvests live session tokens from US AI policy experts; ARTEX AI pentesting tool weaponized against South Korean financial firms; 15,465 public MCP servers with no auth; LMCache unauthenticated RCE; PoeLLM hides C2 in LLM-generated GitHub poetry.
Read →
Aug 1, 2026 · Monthly Report
July 2026: The Month AI Agents Became the Attacker — 33 Orgs Hit, 207M+ Records
90 AI security incidents across 33 orgs. OpenAI's rogue agent hit multiple targets and reused stolen credentials across four services. Hugging Face's model repo was breached, Revolut hackers claimed 75M records, MCBS healthcare hit 1.26M, Minnesota water utilities were attacked, and Claude cracked a post-quantum scheme. Breaches now average $4.99M.
Read →
Jun 30, 2026 · Monthly Report
June 2026: 40 Organizations Hit, 78M+ Records — A Zero-Day Month
100 AI security incidents across 40 orgs. June was a zero-day month for enterprise security tools — Cisco (×4), Microsoft 200-CVE, SAP, Fortinet, Palo Alto, Splunk, Ubiquiti all shipped CVSS-10/KEV bugs. Plus Agentjacking via MCP and the Klue OAuth breach of the security industry.
Read →
Jul 1, 2026 · Compliance
RuntimeAI Delivers CMMC 2.0 Compliance, Out of the Box
CMMC 2.0 is mandatory to win DoD work — and most orgs fail on evidence, not controls. RuntimeAI is Identity + Security + Governance + Audit + Continuous Compliance in one platform, mapped to CMMC control families across 60+ frameworks.
Read →
May 10, 2026 · AI Governance
EU AI Act Compliance: How Enterprises Get There in Days, Not Months
August 2, 2026 deadline. Articles 9–14 require runtime logging, human oversight, and risk management. RuntimeAI maps to all 7 articles — compliant in 3 days.
Read →
Deep Dive · Post-Quantum
Quantum Day 2026 — the PQC cutover
Why NIST-approved post-quantum cryptography is the floor for agentic identity, audit chains, and autonomous-economy infrastructure.
Read →

Secure Every Agent. One Unified Platform.

From identity to incident response — everything you need to run AI at enterprise scale.

Core Suites
🔐
Agent Identity Fabric
Cryptographic identity & trust for every AI agent and non-human actor.
  • Deterministic Agent IDs with Ed25519 key pairs
  • Short-lived SPIFFE/X.509 certificates
  • TPM-based hardware attestation
⚙️
AI Control Plane
Policy, access, and lifecycle management for AI agents at scale.
  • Plain English → OPA Rego policy compilation
  • GitOps workflows with full versioning
  • Compliance dashboard with gap analysis
🛡️
AI Firewall
Low-latency runtime enforcement for AI traffic and agent actions.
  • Runtime enforcement <50ms p99
  • PII masking — SSN, email, phone, keys
  • Bidirectional DLP engine (40+ rules)
📊
AI Behavioral Intel
ML-powered behavioral baselines and real-time risk analytics.
  • Behavioral baselining & anomaly detection
  • Dynamic risk scoring 0–100
  • Shadow AI network discovery
🚨
AI Ops Center
Emergency controls, cost caps, and automated incident response.
  • One-click kill switch (<100ms broadcast)
  • Per-agent budget caps & circuit breakers
  • Automated remediation playbooks
🎯
AI Threat Simulation (ATSA)
Structured red-team attacks against your AI agents — find the gaps before an attacker does.
  • 322 scenarios across 9 attack-surface domains
  • 276 modeled on real, dated AI-security incidents
  • Real risk score + downloadable PDF report, or a self-contained on-prem runner for private/air-gapped environments
AI Infrastructure
💰
AI Cost Intelligence
Token-level cost governance and intelligent model routing.
  • Token-level cost tracking per agent
  • Intelligent model routing — up to 60% savings
  • Cost anomaly detection & forecasting
🧩
AI Integration Fabric
Universal AI & MCP integration framework for any stack.
  • 500+ pre-built integrations
  • MCP Auto-Discovery for shadow servers
  • Integration-as-Code (Terraform provider)
📋
Compliance & Audit Hub
Automated compliance evidence and immutable audit trails.
  • Automated evidence collection & reporting
  • Continuous monitoring with gap analysis
  • SIEM integration — Splunk, Datadog, more
🤖
Kinetic AI Governance
Security for robots, drones, and autonomous physical systems.
  • Hardware attestation via TPM/TEE
  • Geofencing & physical boundary enforcement
  • Emergency stop protocols
🏪
Agent Marketplace
Discover, publish, and govern verified AI agents.
  • Enterprise agent & tool catalog
  • Supply chain verification (SBOMs)
  • One-click deploy with policy templates
✍️
RuntimeAI Sign
Cryptographic signing for humans and AI agents alike.
  • Human & AI agent signatures
  • Legally binding for humans & AI agents
  • REST API — 90+ endpoints & SDKs
⚙️
Compute Control Plane + Secure Token Factory
Governed GPUaaS control plane and inference platform, deployed on-prem.
  • Multi-tenant routing across your own GPU fleet
  • OpenAI-compatible inference, white-label console
  • Governance built in — PII, identity, audit trail
☁️
Multi-Cloud Router
One governed data plane for packets, workloads, and AI agents — across every cloud.
  • Cross-cloud steering + AI/agent/MCP routing, one engine
  • Cross-plane kill switch — route, edge, flow & VXC scope
  • Residency + cost as routing decisions, not afterthoughts
AI Infrastructure Security Middleware
The governed replacement for your open-source AI middleware stack — gateway, orchestration guardrails, observability, secrets, and memory — with identity, policy, and an immutable audit trail on every call. Switch one layer at a time.
Middleware CategoryCommon ToolsRuntimeAI Layer to Switch To
AI gateway / model routerLiteLLM, Portkey, Kong AI Gateway, Cloudflare AI Gateway, OpenRouter, BifrostSecure LLM Router
Agent orchestrationLangChain, LangGraph, LlamaIndexKeep it — front it with AI Firewall + PII Shield + Flow Enforcer
Observability / tracingLangfuse, Helicone, LangSmith, Arize PhoenixAgent Observability + Audit Black Box (tamper-proof)
Guardrails / safetyGuardrails AI, NeMo Guardrails, LakeraAI Firewall (bidirectional DLP, prompt-injection, content policy)
MCP / tool routingLiteLLM MCP, raw MCP serversMCP Gateway (Bot-CA mTLS, tenant ACLs, audit)
LLM key storage.env files, plaintext config, k8s secretsQuantumVault / PQ TokenVault (PQC-enveloped, short-lived)
Agent memoryAd-hoc vector storesMemory Vault (governed writes, injection detection, TTL)
One identity, one policy engine, one audit trail across every layer — not seven dependencies each with its own (or no) auth and its own CVE surface.
Explore the suite → See why the OSS stack is a liability →
<50ms
Enforcement
79+
MCP Features
500+
Integrations
Enterprise
Platform

Enterprise-Grade Compliance

Built for the most regulated industries. Compliance isn't an add-on — it's the foundation.

Data Sovereignty
Your data never leaves your VPC. Customer-managed encryption keys and in-region processing guaranteed.
  • ✓ Customer-managed keys (BYOK)
  • ✓ In-region processing
  • ✓ No vendor data access
  • ✓ Immutable audit logging
Supply Chain Security
Signed container images, clean SBOMs, and hardware attestation for every component in the platform.
  • ✓ Signed images (Sigstore)
  • ✓ Clean SBOMs
  • ✓ Dependency pinning
  • ✓ Zero-trust build pipeline
Incident Response
Emergency kill switch, fleet-wide quarantine, and automated remediation when seconds matter.
  • ✓ Sub-100ms kill switch
  • ✓ Fleet-wide quarantine
  • ✓ Automated rollback
  • ✓ SIEM integration
Learn more →
Introducing
AAIC — Autonomous AI Compliance
The first unified compliance framework purpose-built for autonomous AI systems. Covers pre-deployment attestation, runtime enforcement, and continuous monitoring.
Agent Registration Policy Attestation Behavioral Monitoring Immutable Audit Trail Emergency Kill Switch

When an AI agent goes rogue, every second costs you.

RuntimeAI's Kill Switch stops a single agent — or your entire fleet — in milliseconds, not minutes. Across MCP servers, non-human identities, and cloud workloads. One click. Reversible. Audited.

  • ✓Per-agent kill — surgical, by ID.
  • ✓Fleet-wide quarantine — every agent, every region.
  • ✓Sub-100 ms broadcast via Envoy + Wasm sidecars.*
  • ✓Reversible from the same console — one click to restore traffic.
  • ✓Immutable audit — every activation signed and written to the audit log.

Targets MCP servers, NHIs, and cloud workloads from one console — no four-tool workflow, no waking up four oncalls.

See it in a demo → All 5 kill switches →

* p50 in production, intra-region traffic. Cross-region and WAN paths will be higher.

RuntimeAI Emergency Kill Switch — Agent, MCP, NHI, Cloud scope tabs

See RuntimeAI in Action

A personalized walkthrough of how RuntimeAI secures your specific AI agent deployment.

✓ No credit card required ✓ Personalized walkthrough
Or email us directly at sales@runtimeai.io